Source Intelligence
Overview
Section titled “Overview”The Problem
Section titled “The Problem”80% of REST APIs are undocumented or poorly documented. This also means that 80% of REST APIs are not undergoing security testing since all quality API Security testing tools require a robust OpenAPI Spec (aka Swagger doc) to gain awareness of how to interact with the API and perform tests. However, creating Swagger docs from code requires knowledge of how the code works. Typical strategies include modifying the code to insert code comments, annotations, and decorators and leveraging 3rd party dependencies. If you didn’t write the code, this is time-consuming and difficult.
The Solution
Section titled “The Solution”To remove this friction and enable thorough API security testing against more APIs, NightVision built Source Intelligence, a static analysis engine that extracts OpenAPI specifications from source code. It requires zero code modifications and does not require a running application or code compilation. The engine uses framework-specific knowledge to identify routes and describe how to call them.
Why does this matter?
Section titled “Why does this matter?”Testing undocumented REST APIs with Source Intelligence
Section titled “Testing undocumented REST APIs with Source Intelligence”This helps NightVision perform testing on undocumented REST APIs. Even for a REST API with existing documentation, NightVision often finds endpoints not declared in the existing Swagger docs, allowing NightVision to achieve higher coverage.
Code Traceback
Section titled “Code Traceback”NightVision’s Source Intelligence enables tracing vulnerabilities back to the code origin. When NightVision analyzes code, it annotates the OpenAPI document with the file path and location where each endpoint is declared. When NightVision DAST finds an exploitable vulnerability, NightVision can surface it in GitHub Security Alerts and connect the finding to that code location.
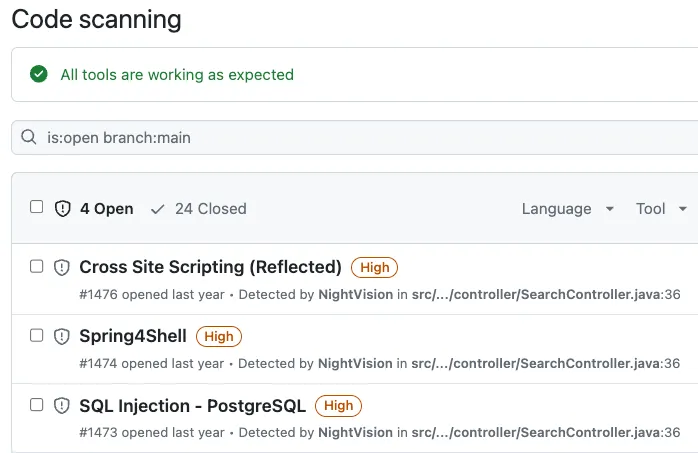
Too often, developers look at code scanning alerts in GitHub or GitLab and ignore them completely - because the results are not exploitable.
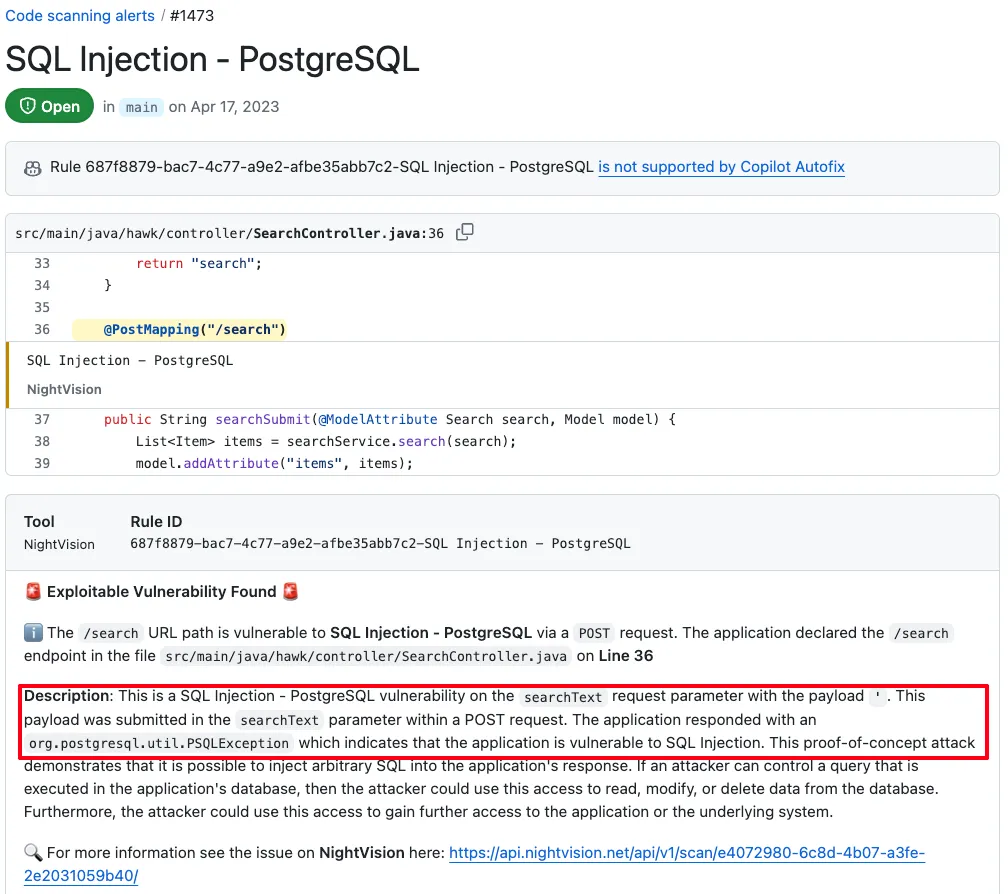
Developers tend to react differently to NightVision’s code scanning alerts because NightVision verifies exploitability. NightVision tells the developer exactly how the vulnerability was exploited.
In the case below, NightVision explains to the developer that NV sent the payload ' to the searchText request parameter in a POST request and getting org.postgresql.util.PSQLException in the response.
Language/Framework Support
Section titled “Language/Framework Support”Across the supported languages, Source Intelligence reads not only routes, parameters, and responses but also the authentication and authorization guards on each endpoint, recording them as OpenAPI security schemes. For more details about supported frameworks, see the Framework Support Index, or visit the details about each language below:
 C#
 Go
 Java
 JavaScript
 PHP
 Python
 Ruby
Tutorial
Section titled “Tutorial”Try the Source Intelligence tutorial, or use the CLI reference to configure an extraction for your own repository:
 Source Intelligence Tutorial