Code Traceback
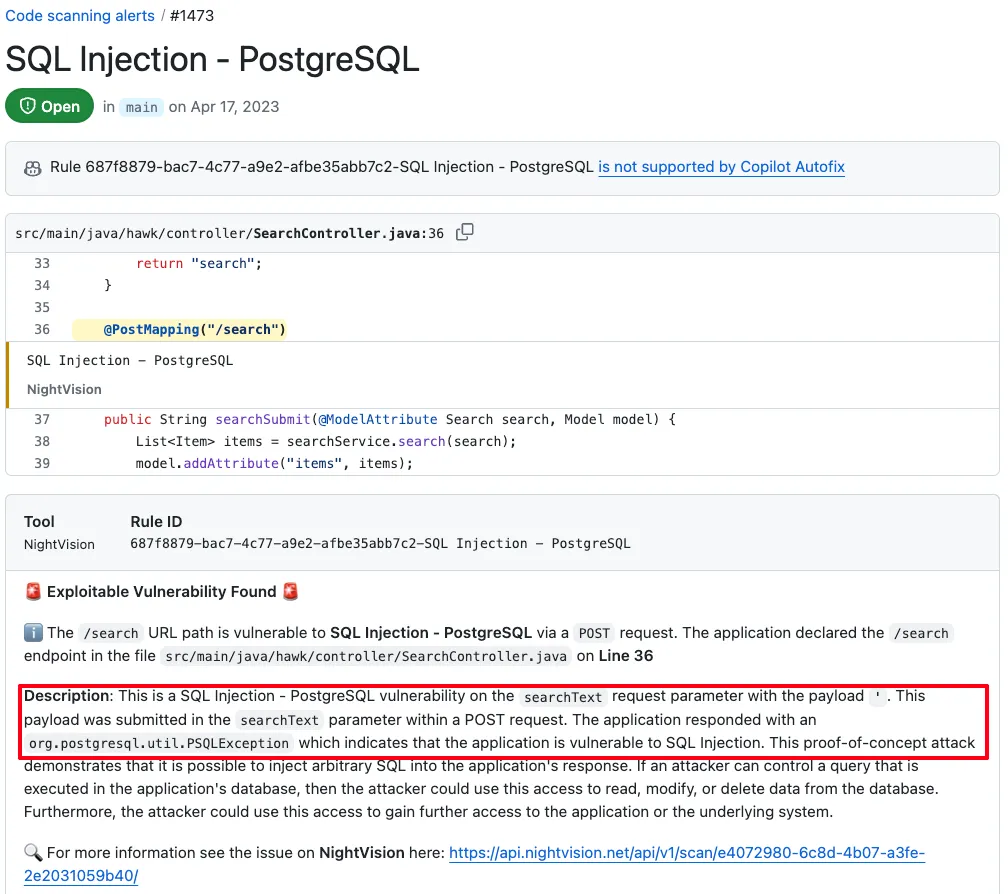
NightVision Source Intelligence enables tracing vulnerabilities back to the code origin. When NightVision analyzes code, it annotates the OpenAPI document with the file path and line where each endpoint is declared. When NightVision DAST finds an exploitable vulnerability, NightVision can surface it in GitHub Security Alerts and connect the finding to that code location.
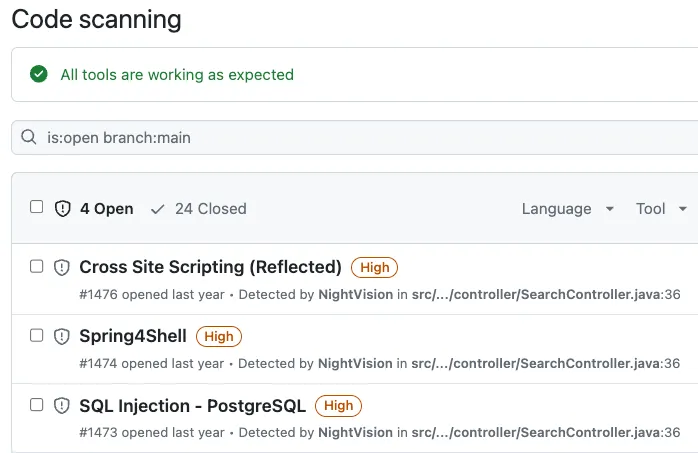
Too often, developers look at code scanning alerts in GitHub or GitLab and ignore them completely - because the results are not exploitable.
Developers tend to react differently to NightVision’s code scanning alerts because NightVision verifies exploitability. NightVision tells the developer exactly how the vulnerability was exploited.
In the case below, NightVision explains to the developer that NV sent the payload ' to the searchText request parameter in a POST request and got org.postgresql.util.PSQLException in the response.
 Code Traceback Tutorial: GitHub Actions